52.70.79.40/32. That is the only address GrowthBook Cloud connects out from — see IP addresses.
SSL and client certificates
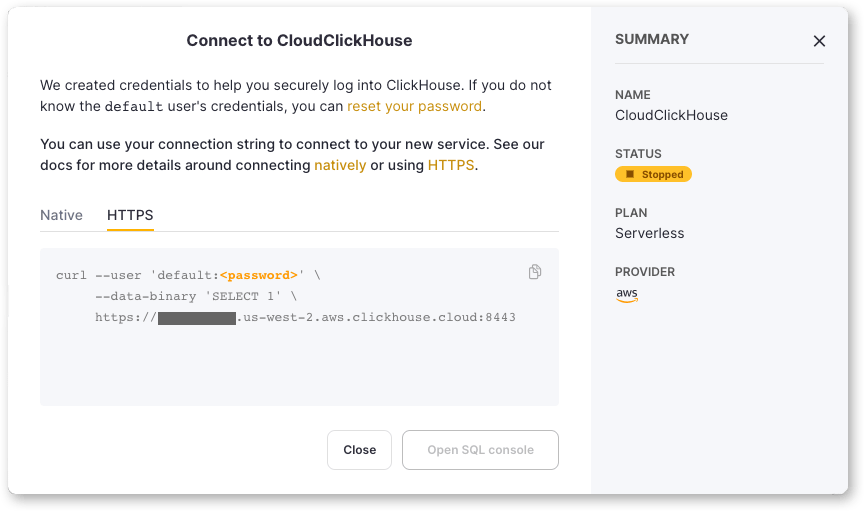
Enable Require SSL to connect over HTTPS. A URL without a scheme defaults tohttps://, and an http:// URL is rejected.
- CA certificate: paste a CA bundle to verify a server with a private or self-signed certificate. Leave it empty to use the default trusted CAs.
- Client certificate and key: paste both to use SSL certificate authentication. GrowthBook sends the username and certificate but not the password. If the certificate is signed by an intermediate CA, paste the leaf followed by its intermediates.
Certificate file paths (self-hosted only)
On a self-hosted GrowthBook with a single organization, you can point GrowthBook at PEM files on its server instead of pasting certificates. Open Certificate file paths under Require SSL and set any of:- CA cert path, Client cert path and Client key path: used instead of the matching pasted value. Set a pasted value or a path for each, not both.
- Client cert chain path (optional): intermediate CA certificates sent after the client certificate. Set this when the client certificate file contains only the leaf and ClickHouse trusts only the root CA. Otherwise the TLS handshake fails with
unknown ca.
subPath mounts, because those aren’t updated when the Secret rotates.